Platform
Services
Solutions
Resources
Company
Offensive & Audit Manager
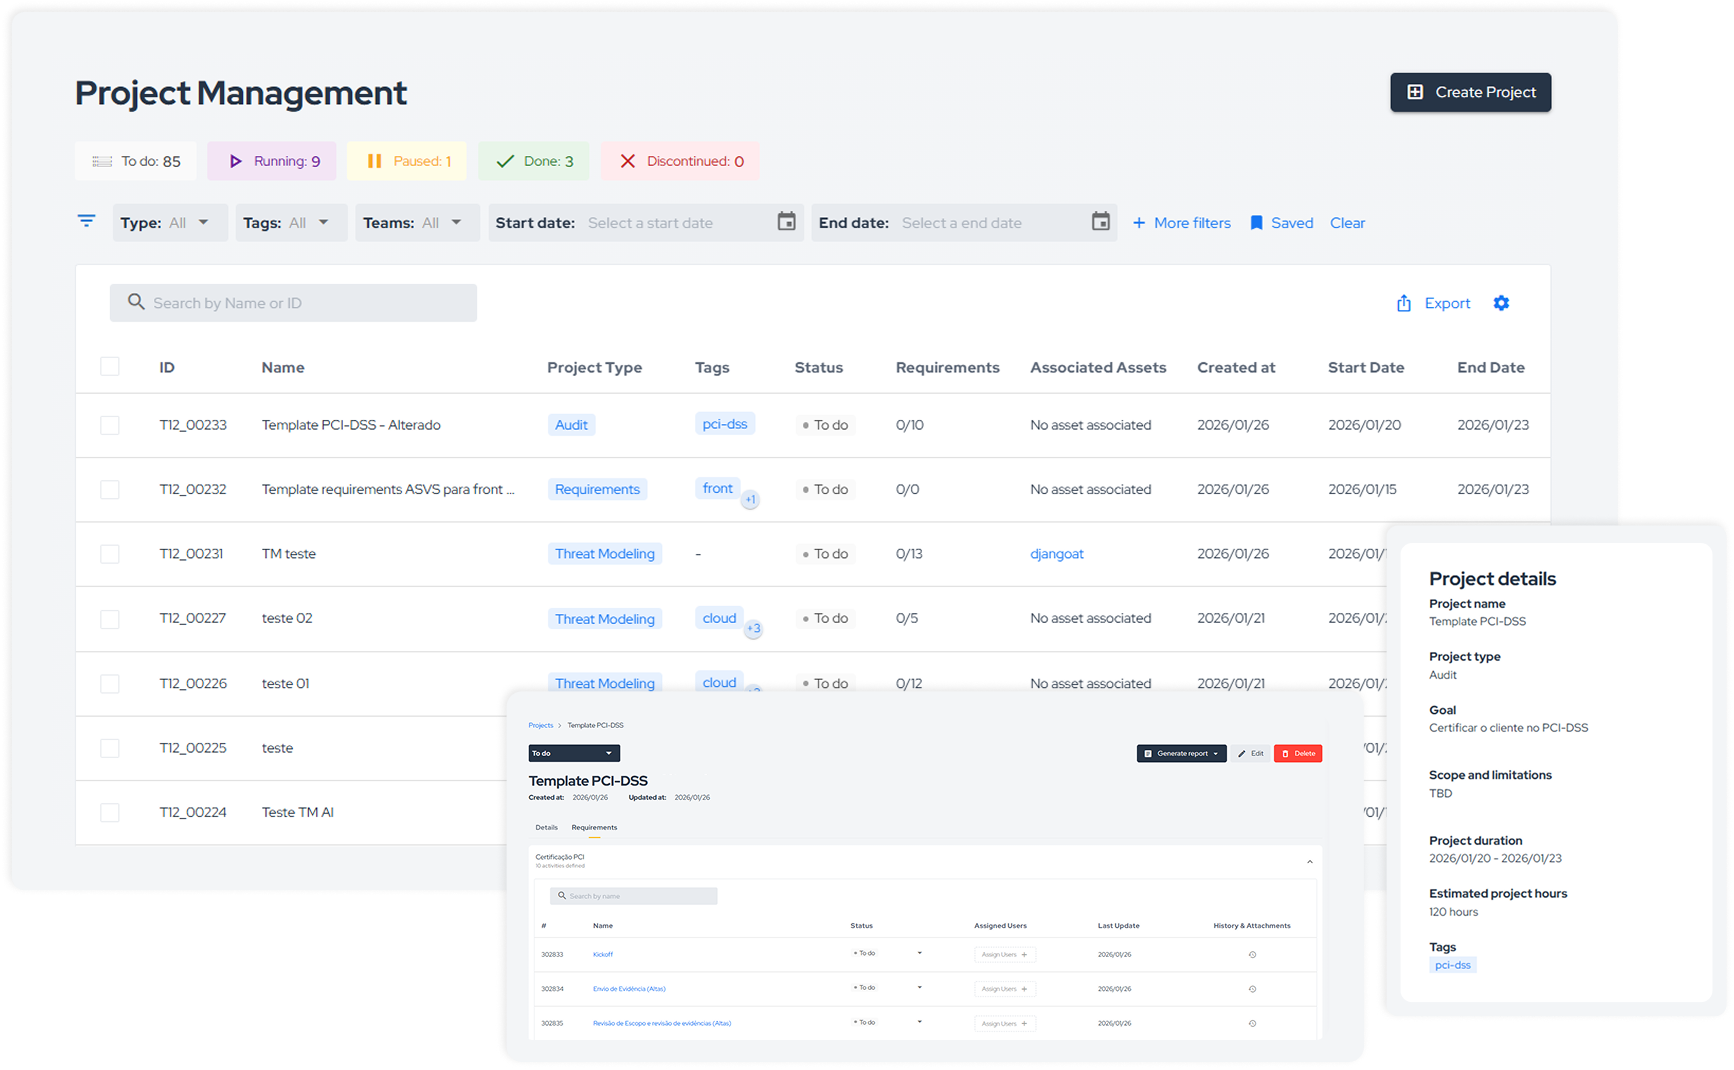
Offensive & Audit Manager brings pentests, offensive security campaigns, and your PCI audit program together in Conviso Platform. Scope becomes trackable requirements, every finding is followed through to the fix, and evidence is ready for each asset, whether the testing is done by your team, outside pentesters, or Conviso experts.
The pentest report is solid. From there, every finding depends on someone copying it into the backlog, and by the next cycle nobody can say for sure what got fixed and what came back.
Multiple assets, multiple testers, and a scope that lives in a stray document. Tracking who tested what, and what they found, turns into coordination work instead of security work.
Your QSA assesses and certifies, but the program behind the certification is scattered across spreadsheets: GAP Self Assessment, evidence, remediation, and the audit trail. It only comes together once the audit is on the calendar.
Offensive & Audit Manager runs offensive work and your audit program as projects, and records everything in the same Conviso Platform vulnerability database.
Every campaign starts as a project, with assets, testers, and requirements defined up front. What needs testing stops being a document and becomes a checklist you can verify.
Your internal team, outside pentesters, Conviso experts, or Autonomous Pentest AI log findings in the same workflow, with evidence tied to each asset.
Findings move to remediation while your PCI program runs alongside them: GAP Self Assessment, internal audits, evidence, and audit records.
One shared history that answers both “what did the pentest find?” and “what does the auditor need to see?”
Each vulnerability from a pentest opens a ticket in Jira or Azure Boards, with priority and context. Automatic status updates when the ticket closes, through two-way sync, are on Advanced and Enterprise plans.
Global Security Gate applies your blocking policy across every asset, so a critical vulnerability found by a pentester blocks the deploy just like one found by a scanner.
Your team runs its own internal audits within the same program and tracks PCI compliance continuously, not just during the certification window.
Every campaign is recorded with its scope, findings, and fixes, and the metrics dashboard shows how things changed from one cycle to the next.
Continuous pentest · Add-on
Autonomous Pentest AI runs pentests on its own against your exposed attack surface, validates each exploit with a proof of concept, and records the attack chain. Findings go straight into Offensive & Audit Manager projects, in the same history as your manual tests, and Offensive & Audit Manager is the most cost-effective way to turn on Autonomous Pentest AI.
Offensive & Audit Manager works on its own, with your internal team, outside pentesters, or alongside Conviso Managed AppSec.
Multiple assets and testers, with scope living in a stray document. Now every campaign is a project, with trackable requirements and evidence for each asset.
GAP Self Assessment, internal audits, evidence, and the audit trail live in spreadsheets today. Now it all runs on one track, from assessment to final evidence.
The report arrives, and control over the findings ends there. Now each finding is logged by the pentester who found it, with a ticket and status through to the fix.
Priced by asset volume in annual tiers. No surprise bills.
Repositories and CI/CD
Ticketing and chat
API and automation
Your QSA assesses and certifies. Someone still has to run the full program between certifications: GAP Self Assessment, internal audits, evidence, remediation, and the audit trail. That's the program Offensive & Audit Manager manages.
Yes. Outside pentesters log findings directly in Conviso Platform, in the same workflow as your internal team.
No. It works with any pentest team. If you want, you can add Conviso experts or Autonomous Pentest AI.
Autonomous Pentest AI runs the pentest; Offensive & Audit Manager runs the program around it. Findings from both live in the same history.
30 minutes with an AppSec specialistBuilt around your organization’s contextNo canned demo